Product Key Explorer 4.2.0.0 – ‘Name’ Denial of Service (POC)
from Exploit-DB.com RSS Feed https://ift.tt/2YBHQsp
via IFTTT
Product Key Explorer 4.2.0.0 – ‘Name’ Denial of Service (POC)
from Exploit-DB.com RSS Feed https://ift.tt/2YBHQsp
via IFTTT
Ad-blocking technologies can block the cookies that record consumers’ privacy choices, they claim.
from Naked Security https://ift.tt/2scRwgX
via IFTTT
Microsoft today released updates to plug three dozen security holes in its Windows operating system and other software. The patches include fixes for seven critical bugs — those that can be exploited by malware or miscreants to take control over a Windows system with no help from users — as well as another flaw in most versions of Windows that is already being exploited in active attacks.
 By nearly all accounts, the chief bugaboo this month is CVE-2019-1458, a vulnerability in a core Windows component (Win32k) that is present in Windows 7 through 10 and Windows Server 2008-2019. This bug is already being exploited in the wild, and according to Recorded Future the exploit available for it is similar to CVE-2019-0859, a Windows flaw reported in April that was found being sold in underground markets.
CVE-2019-1458 is what’s known as a “privilege escalation” flaw, meaning an attacker would need to previously have compromised the system using another vulnerability. Handy in that respect is CVE-2019-1468, a similarly widespread critical issue in the Windows font library that could be exploited just by getting the user to visit a hacked or malicious Web site.
Chris Goettl, director of security at Ivanti, called attention to a curious patch advisory Microsoft released today for CVE-2019-1489, which is yet another weakness in the Windows Remote Desktop Protocol (RDP) client, a component of Windows which lets users view and manage their system from a remote computer. What’s curious about this advisory is that it applies only to Windows XP Service Pack 3, which is no longer receiving security updates.
“The Exploitability Assessment for Latest Software Release and Older Software Release is 0, which is usually the value reserved for a vulnerability that is known to be exploited, yet the Exploited value was currently set to ‘No’ as the bulletin was released today,” Goettl said. “If you look at the Zero Day from this month (CVE-2019-1458) the EA for Older Software Release is ‘0 – Exploitation Detected.’ An odd discrepancy on top of a CVE advisory for an outdated OS. It is very likely this is being exploited in the wild.”
Microsoft didn’t release a patch for this bug on XP, and its advisory on it is about as sparse as they come. But if you’re still depending on Windows XP for remote access, you likely have bigger security concerns. Microsoft has patched many critical RDP flaws in the past year. Even the FBI last year encouraged users to disable it unless needed, citing flawed encryption mechanisms in older versions and a lack of access controls which make RDP a frequent entry point for malware and ransomware.
Speaking of no-longer-supported Microsoft operating systems, Windows 7 and Windows Server 2008 will cease receiving security updates after the next decade’s first Patch Tuesday comes to pass on January 14, 2020. While businesses and other volume-license purchasers will have the option to pay for further fixes after that point, all other Windows 7 users who want to stick with Windows will need to consider migrating to Windows 10 soon.
Windows 10 likes to install patches and sometimes feature updates all in one go and reboot your computer on its own schedule, but you don’t have to accept this default setting. Windows Central has a useful guide on how to disable or postpone automatic updates until you’re ready to install them. For all other Windows OS users, if you’d rather be alerted to new updates when they’re available so you can choose when to install them, there’s a setting for that in Windows Update. To get there, click the Windows key on your keyboard and type “windows update” into the box that pops up.
Keep in mind that while staying up-to-date on Windows patches is a good idea, it’s important to make sure you’re updating only after you’ve backed up your important data and files. A reliable backup means you’re probably not losing your mind when the odd buggy patch causes problems booting the system. So do yourself a favor and backup your files before installing any patches.
And as always, if you experience glitches or problems installing any of these patches this month, please consider leaving a comment about it below; there’s a better-than-even chance other readers have experienced the same and may even chime in here with some helpful tips.
Finally, once again there are no security updates for Adobe Flash Player this month (there is a non-security update available), but Adobe did release critical updates for Windows and macOS versions of its Acrobat and PDF Reader that fix more than 20 vulnerabilities in these products. Photoshop and ColdFusion 2018 also received security updates today. Links to advisories here.
from Krebs on Security https://ift.tt/2sgIz5Y
via IFTTT
A total of 2.7 billion email addresses, 1 billion email account passwords, and nearly 800,000 applications for copies of birth certificate were found on unsecured cloud buckets.
from Dark Reading: https://ift.tt/38ruPWL
via IFTTT
This month’s batch of security updates addresses 36 CVEs, seven of which are rated Critical and one of which has been exploited in the wild.
from Dark Reading: https://ift.tt/2LFkfBW
via IFTTT
Researchers found three broad types of vulnerabilities, one of which should be particularly concerning to consumers.
from Dark Reading: https://ift.tt/2t3qYip
via IFTTT
A breakdown of the common ways criminals employ MitM techniques to snare victims, and tips for protecting users from these dirty tricks.
from Dark Reading: https://ift.tt/2LKrRTI
via IFTTT
We can’t wait out this problem and hope that it goes away. We must be proactive.
from Dark Reading: https://ift.tt/3428VWM
via IFTTT
CISO Magazine, a publication dedicated to covering issues near and dear to corporate chief information security officers everywhere, has graciously awarded this author the designation of “Cybersecurity Person of the Year” in its December 2019 issue.
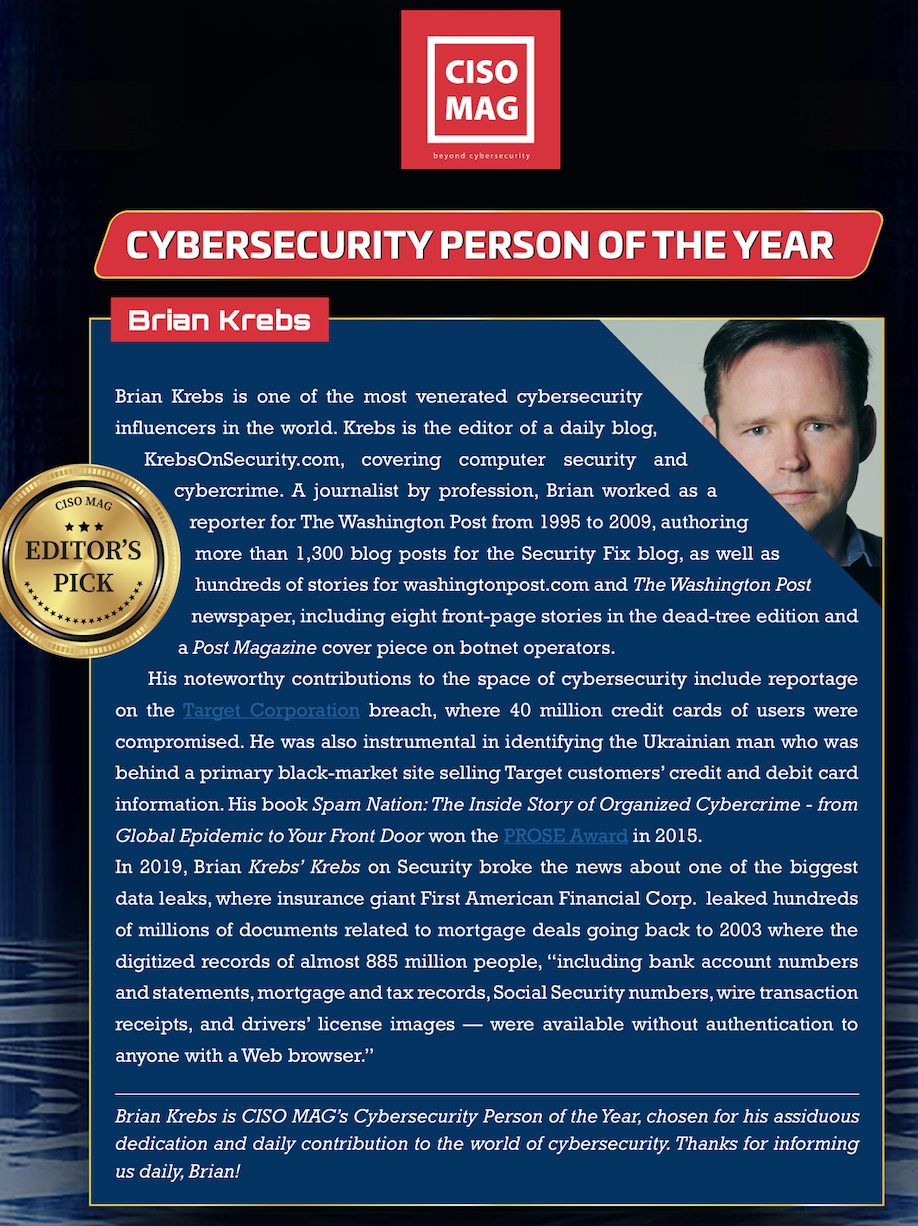 KrebsOnSecurity is grateful for the unexpected honor. But I can definitely think of quite a few people who are far more deserving of this title. In fact, if I’m eligible for any kind of recognition, perhaps “Bad News Harbinger of the Year” would be more apt.
As in years past, 2019 featured quite a few big breaches and more than a little public speaking. Almost without fail at each engagement multiple C-level folks will approach after my talk, hand me their business cards and say something like, “I hope you never have to use this, but if you do please call me first.”
I’ve taken that advice to heart, and now endeavor wherever possible to give a heads up to CISOs/CSOs about a breach before reaching out to the public relations folks. I fully realize that in many cases the person in that role will refer me to the PR department eventually or perhaps immediately.
But on balance, my experience so far is that an initial outreach to the top security person in the organization often results in that inquiry being taken far more seriously. And including this person in my initial outreach makes it much more likely that this individual ends up being on the phone when the company returns my call.
Too often, these conversations are led by the breached organization’s general counsel, which strikes me as an unnecessarily confrontational and strategically misguided approach. Especially if this is also their playbook for responding to random security researchers trying to let the company know about a dangerous security vulnerability, data breach or leak.
At least when there is a C-level security person on the phone when that call comes in I can be relatively sure I’m not going to get snowed on the technical details. While this may a distant concern for the organization in the throes of responding to a data security incident, the truth is that the first report is usually what gets repeated in the media — whether or not it is wholly accurate or fair.
This year’s CISO Magazine awards also honor the contributions of Rik Ferguson, vice president security research at Trend Micro, and Troy Hunt, an expert on web security and author of the data breach search website Have I Been Pwned? More at cisomag.com.
from Krebs on Security https://ift.tt/36l5z2E
via IFTTT
Most practitioners report an increase in identities, but many don’t have control over how those identities are protected from a range of attacks.
from Dark Reading: https://ift.tt/38pY2kY
via IFTTT

