You could be making millions in just two years!
from Dark Reading: https://ift.tt/2vMwgjW
via IFTTT
You could be making millions in just two years!
from Dark Reading: https://ift.tt/2vMwgjW
via IFTTT
A humorous nod to the lack of gender equity in cybersecurity hiring was our judges’ unanimous choice. And the winners are …
from Dark Reading: https://ift.tt/32bGeY3
via IFTTT
When a user interacts with an enterprise system the result can be productivity or disaster. Here are 8 opportunities for the disaster side to win out over the productive.
from Dark Reading: https://ift.tt/32bBotR
via IFTTT
Ten days after a suspected ransomware attack, residents of the English borough of Redcar and Cleveland must be starting to wonder when their Council’s IT systems will return.
from Naked Security https://ift.tt/38BIkmo
via IFTTT
A small but determined group of Twitter users think it is a good idea to direct message (DM) pictures of male genitals to complete strangers.
from Naked Security https://ift.tt/327zlqx
via IFTTT
Popular cryptocurrency IOTA has temporarily shut down its entire network after a hacker stole funds from ten of its highest-value users.
from Naked Security https://ift.tt/3bN0iEB
via IFTTT
Researchers at VPN advisory company vpnMentor have found yet another online data exposure caused by a misconfigured cloud database.
from Naked Security https://ift.tt/2Hzz1ru
via IFTTT
WordPress Plugin WP Sitemap Page 1.6.2 – Persistent Cross-Site Scripting
from Exploit-DB.com RSS Feed https://ift.tt/2wlWWbi
via IFTTT
The same hackers have also got their mitts on social media accounts of other high-profile sporting targets
The post FC Barcelona Twitter account hacked – again appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/37yxQ65
via IFTTT
A new email-based extortion scheme apparently is making the rounds, targeting Web site owners serving banner ads through Google’s AdSense program. In this scam, the fraudsters demand bitcoin in exchange for a promise not to flood the publisher’s ads with so much bot and junk traffic that Google’s automated anti-fraud systems suspend the user’s AdSense account for suspicious traffic.
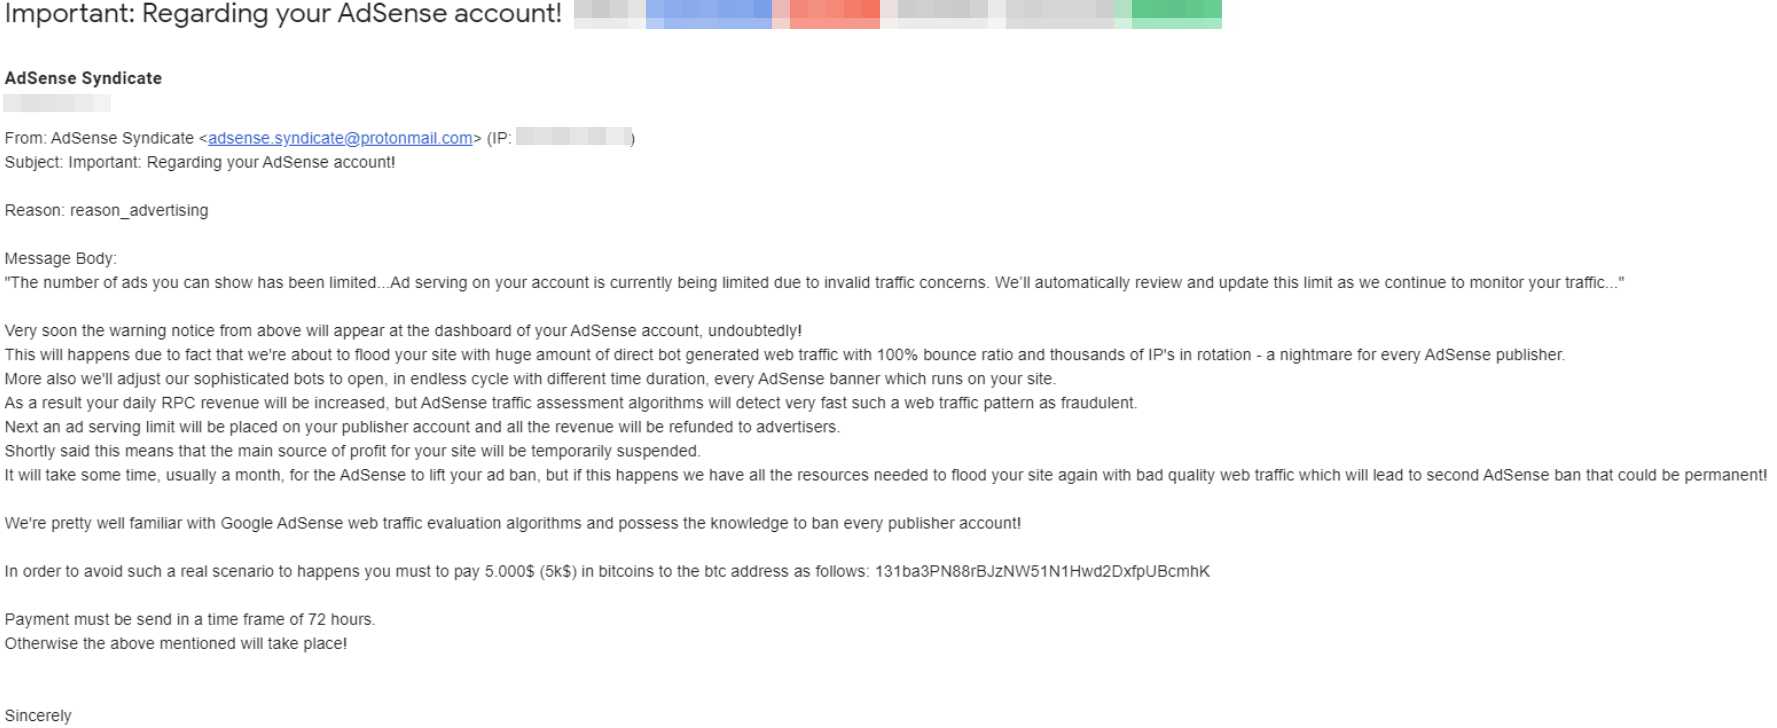
A redacted extortion email targeting users of Google’s AdSense program.
Earlier this month, KrebsOnSecurity heard from a reader who maintains several sites that receive a fair amount of traffic. The message this reader shared began by quoting from an automated email Google’s systems might send if they detect your site is seeking to benefit from automated clicks. The message continues:
“Very soon the warning notice from above will appear at the dashboard of your AdSense account undoubtedly! This will happen due to the fact that we’re about to flood your site with huge amount of direct bot generated web traffic with 100% bounce ratio and thousands of IP’s in rotation — a nightmare for every AdSense publisher. More also we’ll adjust our sophisticated bots to open, in endless cycle with different time duration, every AdSense banner which runs on your site.”
The message goes on to warn that while the targeted site’s ad revenue will be briefly increased, “AdSense traffic assessment algorithms will detect very fast such a web traffic pattern as fraudulent.”
“Next an ad serving limit will be placed on your publisher account and all the revenue will be refunded to advertisers. This means that the main source of profit for your site will be temporarily suspended. It will take some time, usually a month, for the AdSense to lift your ad ban, but if this happens we will have all the resources needed to flood your site again with bad quality web traffic which will lead to second AdSense ban that could be permanent!”
The message demands $5,000 worth of bitcoin to forestall the attack. In this scam, the extortionists are likely betting that some publishers may see paying up as a cheaper alternative to having their main source of advertising revenue evaporate.
The reader who shared this email said while he considered the message likely to be a baseless threat, a review of his recent AdSense traffic statistics showed that detections in his “AdSense invalid traffic report” from the past month had increased substantially.
The reader, who asked not to be identified in this story, also pointed to articles about a recent AdSense crackdown in which Google announced it was enhancing its defenses by improving the systems that identify potentially invalid traffic or high risk activities before ads are served.
Google defines invalid traffic as “clicks or impressions generated by publishers clicking their own live ads,” as well as “automated clicking tools or traffic sources.”
“Pretty concerning, thought it seems this group is only saying they’re planning their attack,” the reader wrote.
Google declined to discuss this reader’s account, saying its contracts prevent the company from commenting publicly on a specific partner’s status or enforcement actions. But in a statement shared with KrebsOnSecurity, the company said the message appears to be a classic threat of sabotage, wherein an actor attempts to trigger an enforcement action against a publisher by sending invalid traffic to their inventory.
“We hear a lot about the potential for sabotage, it’s extremely rare in practice, and we have built some safeguards in place to prevent sabotage from succeeding,” the statement explained. “For example, we have detection mechanisms in place to proactively detect potential sabotage and take it into account in our enforcement systems.”
Google said it has extensive tools and processes to protect against invalid traffic across its products, and that most invalid traffic is filtered from its systems before advertisers and publishers are ever impacted.
“We have a help center on our website with tips for AdSense publishers on sabotage,” the statement continues. “There’s also a form we provide for publishers to contact us if they believe they are the victims of sabotage. We encourage publishers to disengage from any communication or further action with parties that signal that they will drive invalid traffic to their web properties. If there are concerns about invalid traffic, they should communicate that to us, and our Ad Traffic Quality team will monitor and evaluate their accounts as needed.”
from Krebs on Security https://ift.tt/3bEAzOF
via IFTTT

