Listen to the latest episode now!
from Naked Security https://ift.tt/3baAQI3
via IFTTT
Listen to the latest episode now!
from Naked Security https://ift.tt/3baAQI3
via IFTTT
Trolls have been joining videoconferencing calls to expose meeting participants to disturbing videos.
from Naked Security https://ift.tt/2J1B87Z
via IFTTT
How can employees stay motivated and productive while teleworking during the COVID-19 crisis?
The post Keep calm and carry on working (remotely) appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/2J2mWeT
via IFTTT
Online exchange rate data provider Open Exchange Rates has exposed an undisclosed amount of user data via an Amazon database.
from Naked Security https://ift.tt/2U6QkXO
via IFTTT
In February, hardware maker Zyxel fixed a zero-day vulnerability in its routers and VPN firewall products after KrebsOnSecurity told the company the flaw was being abused by attackers to break into devices. This week, security researchers said they spotted that same vulnerability being exploited by a new variant of Mirai, a malware strain that targets vulnerable Internet of Things (IoT) devices for use in large-scale attacks and as proxies for other cybercrime activity.
Security experts at Palo Alto Networks said Thursday their sensors detected the new Mirai variant — dubbed Mukashi — on Mar. 12. The new Mirai strain targets CVE-2020-9054, a critical flaw that exists in many VPN firewalls and network attached storage (NAS) devices made by Taiwanese vendor Zyxel Communication Corp., which boasts some 100 million devices deployed worldwide.
Like other Mirai variants, Mukashi constantly scans the Internet for vulnerable IoT devices like security cameras and digital video recorders (DVRs), looking for a range of machines protected only by factory-default credentials or commonly-picked passwords.
Palo Alto said IoT systems infected by Mukashi then report back to a control server, which can be used to disseminate new instructions — such as downloading additional software or launching distributed denial of service (DDoS) attacks.
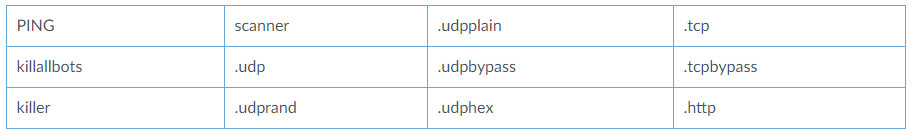
The commands Mukashi botmasters can send to infected devices include scanning for and exploiting other systems, and launching DDoS attacks. Image: Palo Alto Networks.
Zyxel issued a patch for the flaw on Feb. 24, but the update did not fix the problem on many older Zyxel devices which are no longer being supported by the company. For those devices, Zyxel’s advice was not to leave them connected to the Internet.
A joint advisory on CVE-2020-9054 from the U.S. Department of Homeland Security and the CERT Coordination Center rates this vulnerability at a “10” — the most severe kind of flaw. The DHS/CERT advisory also includes sample code to test if a Zyxel product is vulnerable to the flaw.
My advice? If you can’t patch it, pitch it, as Mukashi is not the only thing interested in this Zyxel bug: Recent activity suggests attackers known for deploying ransomware have been actively working to test it for use against targets.
from Krebs on Security https://ift.tt/3bgYaE7
via IFTTT
They don’t predict breaches, and they don’t help people make valuable business decisions or make users any safer.
from Dark Reading: https://ift.tt/2WvTKVu
via IFTTT
In typical fashion, attackers are gearing up to take advantage of the surge in teleworking prompted by the pandemic.
from Dark Reading: https://ift.tt/2vyQYno
via IFTTT
It’s the COVID-19 shortage nobody expected – not toilet rolls, tinned goods or headache pills this time but Google software engineers.
from Naked Security https://ift.tt/2J4b2RW
via IFTTT
The government says the wristband isn’t privacy-invading because it won’t track your location, per se; just if you wander from COVID-19 quarantine.
from Naked Security https://ift.tt/38ZDFdu
via IFTTT
Losing access to your account can be stressful, but there are steps you can take to get it back – and to avoid getting hacked again
The post What to do if your Twitter account has been hacked appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/2QAptBo
via IFTTT

