from Dark Reading: https://ift.tt/3hMz4B9
via IFTTT
Tag Archives: Cybersecurity
Bundlore adware brings a new nest of risks to Mac users
A new SophosLabs report digs into the latest browser-hijacking “bundleware” targeting Mac users
from Naked Security https://ift.tt/3hIgCcu
via IFTTT
CISO Dialogue: How to Optimize Your Security Budget
CISOs are never going to have all the finances they want. Hard choices must be made. The CISO of Amazon Prime Video discusses his approaches to a slimmed-down budget.
from Dark Reading: https://ift.tt/3fFYDl9
via IFTTT
Crypto founder admits $25 million ICO backed by celebrities was a scam
Endorsed by boxer Floyd Mayweather and DJ Khaled, the Centra Tech ICO debacle has led to the guilty plea of co-founder Robert Farkas.
from Naked Security https://ift.tt/2Cb8cdt
via IFTTT
Adobe drops slew of critical patches
Adobe released another set of patches for its products on Tuesday, a week after dropping its first set of fixes for the month.
from Naked Security https://ift.tt/2YKsW3B
via IFTTT
Ripple20 bugs expose hundreds of millions of devices to attacks
Devices used in the energy, transportation and communications sectors are also affected by the flaws in the TCP/IP software library
The post Ripple20 bugs expose hundreds of millions of devices to attacks appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/2UOVXKf
via IFTTT
Operation In(ter)ception: Aerospace and military companies in the crosshairs of cyberspies
ESET researchers uncover targeted attacks against high-profile aerospace and military companies
The post Operation In(ter)ception: Aerospace and military companies in the crosshairs of cyberspies appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/3dboj7A
via IFTTT
When Security Takes a Backseat to Productivity
“We must care as much about securing our systems as we care about running them if we are to make the necessary revolutionary change.” -CIA’s Wikileaks Task Force.
So ends a key section of a report the U.S. Central Intelligence Agency produced in the wake of a mammoth data breach in 2016 that led to Wikileaks publishing thousands of classified documents stolen from the agency’s offensive cyber operations division. The analysis highlights a shocking series of security failures at one of the world’s most secretive organizations, but the underlying weaknesses that gave rise to the breach also unfortunately are all too common in many organizations today.
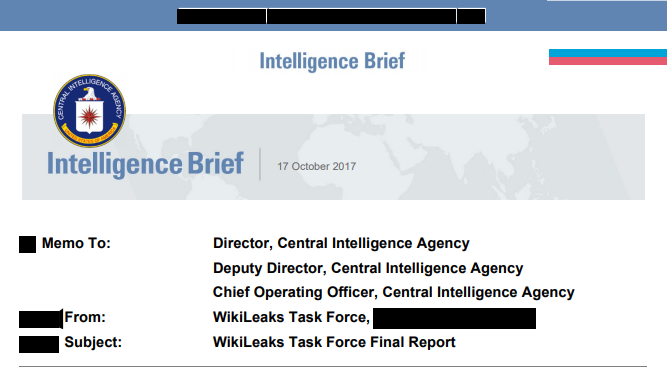
The CIA produced the report in October 2017, roughly seven months after Wikileaks began publishing Vault 7 — reams of classified data detailing the CIA’s capabilities to perform electronic surveillance and cyber warfare. But the report’s contents remained shrouded from public view until earlier this week, when heavily redacted portions of it were included in a letter by Sen. Ron Wyden (D-Ore.) to the Director of National Intelligence.
The CIA acknowledged its security processes were so “woefully lax” that the agency probably would never have known about the data theft had Wikileaks not published the stolen documents online. What kind of security failures created an environment that allegedly allowed a former CIA employee to exfiltrate so much sensitive data? Here are a few, in no particular order:
- Failing to rapidly detect security incidents.
- Failing to act on warning signs about potentially risky employees.
- Moving too slowly to enact key security safeguards.
- A lack of user activity monitoring or robust server audit capability.
- No effective removable media controls.
- No single person empowered to ensure IT systems are built and maintained securely throughout their lifecycle.
- Historical data available to all users indefinitely.
Substitute the phrase “cyber weapons” with “productivity” or just “IT systems” in the CIA’s report and you might be reading the post-mortem produced by a security firm hired to help a company recover from a highly damaging data breach.
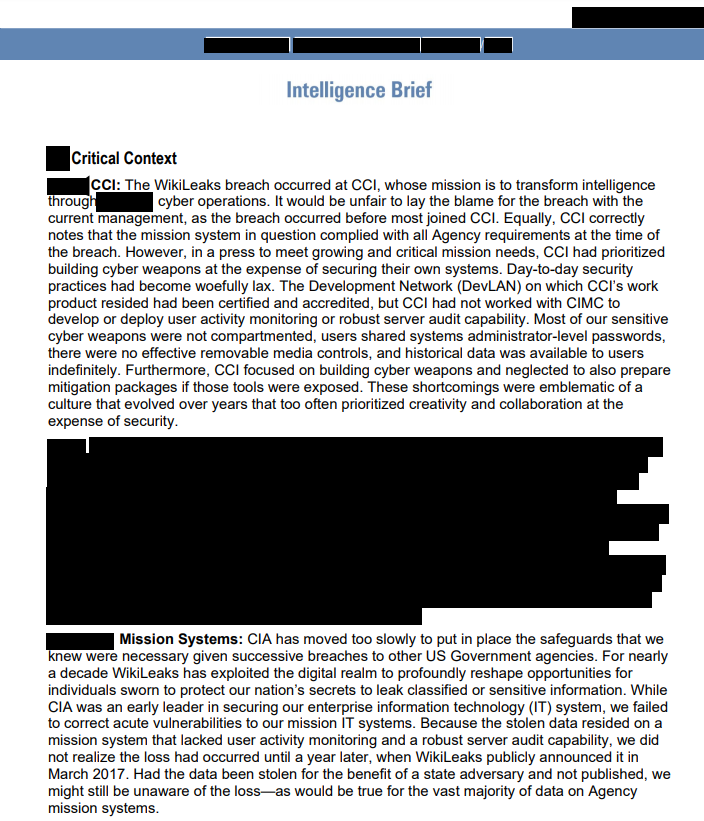
A redacted portion of the CIA’s report on the Wikileaks breach.
DIVIDED WE STAND, UNITED WE FALL
A key phrase in the CIA’s report references deficiencies in “compartmentalizing” cybersecurity risk. At a high level (not necessarily specific to the CIA), compartmentalizing IT environments involves important concepts such as:
- Segmenting one’s network so that malware infections or breaches in one part of the network can’t spill over into other areas.
- Not allowing multiple users to share administrative-level passwords
- Developing baselines for user and network activity so that deviations from the norm stand out more prominently.
- Continuously inventorying, auditing, logging and monitoring all devices and user accounts connected to the organization’s IT network.
“The Agency for years has developed and operated IT mission systems outside the purview and governance of enterprise IT, citing the need for mission functionality and speed,” the CIA observed. “While often fulfilling a valid purpose, this ‘shadow IT’ exemplifies a broader cultural issue that separates enterprise IT from mission IT, has allowed mission system owners to determine how or if they will police themselves.”
All organizations experience intrusions, security failures and oversights of key weaknesses. In large enough enterprises, these failures likely happen multiple times each day. But by far the biggest factor that allows small intrusions to morph into a full-on data breach is a lack of ability to quickly detect and respond to security incidents.
Also, because employees tend to be the most abundant security weakness in any organization, instituting some kind of continuing security awareness training for all employees is a good idea. Some security experts I know and respect dismiss security awareness programs as a waste of time and money, observing that no matter how much training a company does, there will always be some percentage of users who will click on anything.
That may or may not be accurate, but even if it is, at least the organization then has a much better idea which employees probably need more granular security controls (i.e. more compartmentalizing) to keep them from becoming a serious security liability.
Sen. Wyden’s letter (PDF), first reported on by The Washington Post, is worth reading because it points to a series of continuing security weaknesses at the CIA, many of which have already been addressed by other federal agencies, including multi-factor authentication for domain names and access to classified/sensitive systems, and anti-spam protections like DMARC.
from Krebs on Security https://ift.tt/2Y91CwL
via IFTTT
7 Tips for Employers Navigating Remote Recruitment
Hiring experts explain how companies should approach recruitment when employers and candidates are working remotely.
from Dark Reading: https://ift.tt/2ClwYbb
via IFTTT
Zoom Changes Course on End-to-End Encryption
The videoconferencing company now says it will offer end-to-end encryption to all users beginning in July.
from Dark Reading: https://ift.tt/2UTNLsi
via IFTTT

