Deal gives Sophos a new AI-based cloud security platform.
from Dark Reading: https://ubm.io/2VCTzow
via IFTTT
Deal gives Sophos a new AI-based cloud security platform.
from Dark Reading: https://ubm.io/2VCTzow
via IFTTT
Wireshark – ‘get_t61_string’ Heap Out-of-Bounds Read
from Exploit-DB.com RSS Feed http://bit.ly/2FbUMhT
via IFTTT
The recently disclosed Marriott breach exposed a frequently ignored issue in the M&A process.
from Dark Reading: https://ubm.io/2Cb19xK
via IFTTT
Dolibarr ERP-CRM 8.0.4 – ‘rowid’ SQL Injection
from Exploit-DB.com RSS Feed http://bit.ly/2sfhzR5
via IFTTT
Buying heavily discounted, popular software from second-hand sources online has always been something of an iffy security proposition. But purchasing steeply discounted licenses for cloud-based subscription products like recent versions of Microsoft Office can be an extremely risky transaction, mainly because you may not have full control over who has access to your data.
Last week, KrebsOnSecurity heard from a reader who’d just purchased a copy of Microsoft Office 2016 Professional Plus from a seller on eBay for less than $4. Let’s call this Red Flag #1, as a legitimately purchased license of Microsoft Office 2016 is still going to cost between $70 and $100. Nevertheless, almost 350 other people had made the same purchase from this seller over the past year, according to eBay, and there appear to be many auctioneers just like this one.
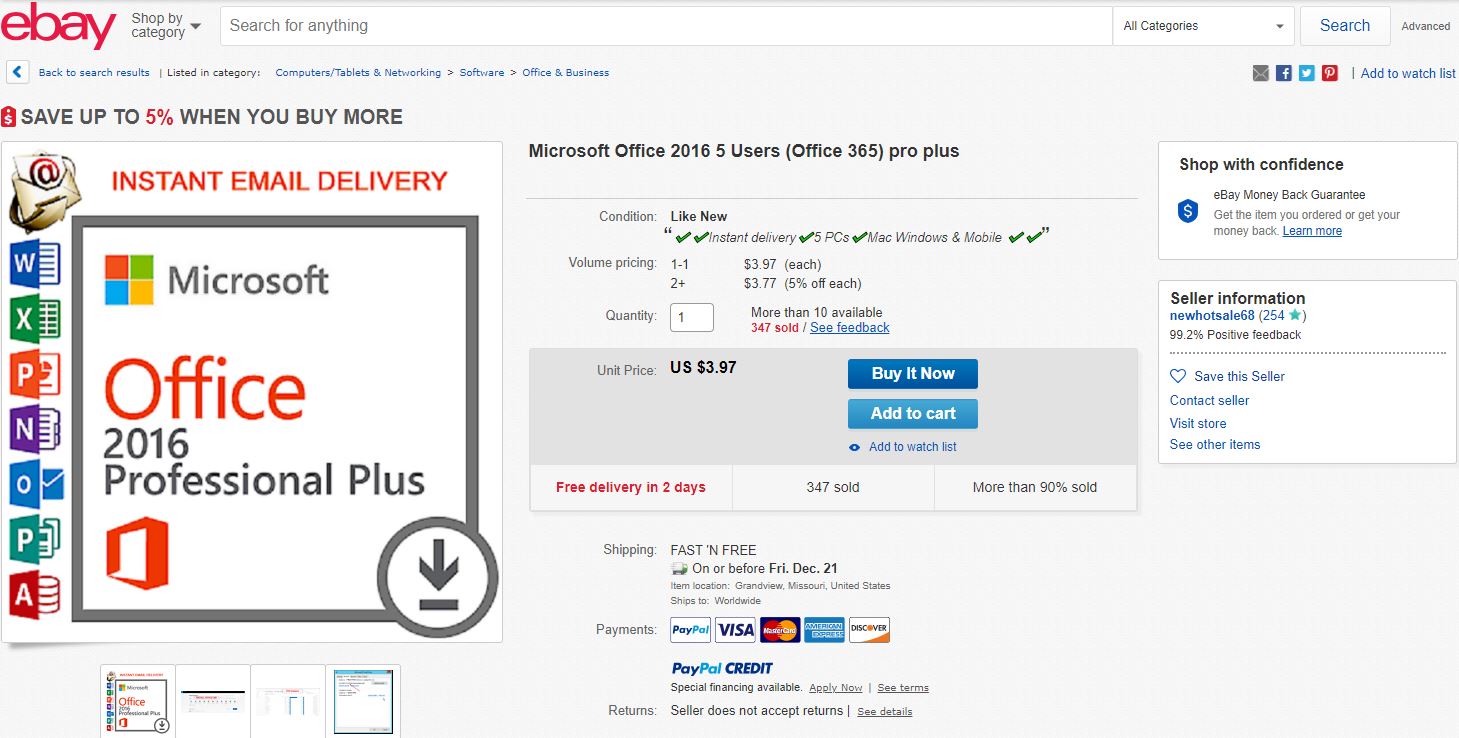
After purchasing the item, the buyer said he received the following explanatory (exclamatory?) email from the seller — “Newhotsale68” from Vietnam:
Hello my friend!
Thank you for your purchase:)Very important! Office365 is a subscription product and does not require any KEY activation. Account + password = free lifetime use
1. Log in with the original password and the official website will ask you to change your password!
2. Be sure to remember the modified new password. Once you forget your password, you will lose Office365!
3. After you change your password, log on to the official website to start downloading and installing Office365!
Your account information:
* USERMANE : (sent username)
Password Initial: (sent password)
Microsoft Office 365 access link:
Sounds legit, right?
This merchant appears to be reselling access to existing Microsoft Office accounts, because in order to use this purchase the buyer must log in to Microsoft’s site using someone else’s username and password! Let’s call this Red Flag #2.
More importantly, the buyer can’t change the email address associated with the license, which means whoever owns that address can likely still assume control over any licenses tied to it. We’ll call this Ginormous Red Flag #3.
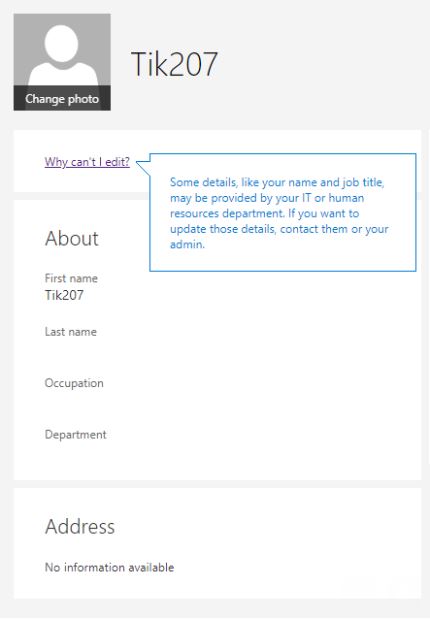
“The username that you use to register and activate Office is one that they provide to you in their email when you buy the license on eBay,” wrote the reader who alerted me about this dodgy transaction. “You never use your own email account to register, you have to log in with theirs. Once you’re inside the account you can’t change the username to your email account because the admin locked it down.”
Here’s what the profile looked like when the reader tried to change details tied to the license.
This version of Office prompts the user to sync all data and documents over to a 5TB Microsoft OneDrive account. What could go wrong?
“You can sign out of their Microsoft account to break the connection to the OneDrive account,” the reader said. “By default it had me signed in and I bet most people installing this just click next and stay signed in.”
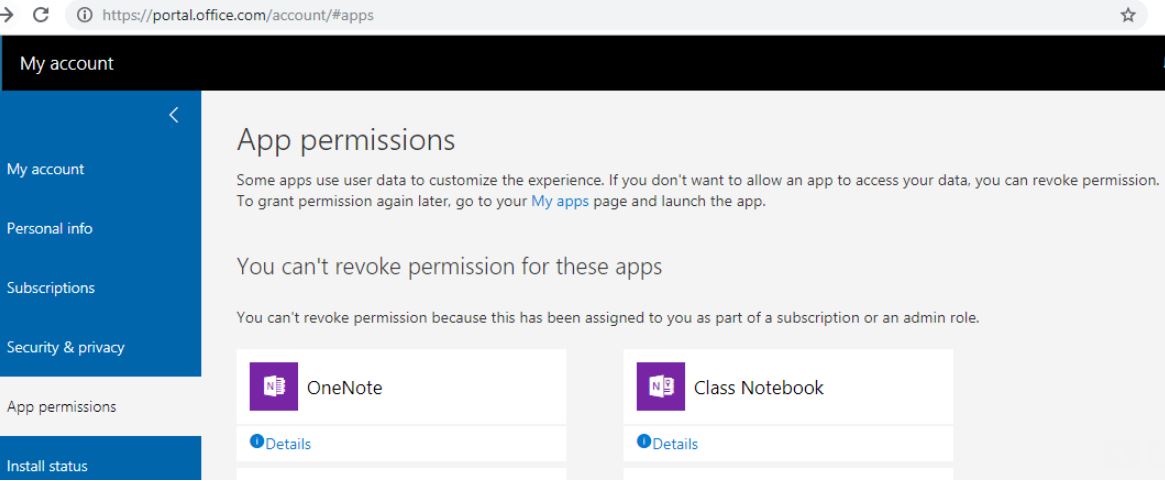
That’s not all: The account was set up so that the administrator (seller) maintained control over specific apps on the Office installation, including OneNote and Class Notebook.
“I guess maybe the end result of all of this are the old adages, ‘you get what you pay for’ and, ‘if it sounds too good to be true than it probably is,’” the reader said at the conclusion of his email.
Couldn’t have said it better myself.
from Krebs on Security http://bit.ly/2RzR3QS
via IFTTT
CF Image Hosting Script 1.6.5 – (Delete all Pictures) Privilege Escalation
from Exploit-DB.com RSS Feed http://bit.ly/2VCv6Ql
via IFTTT
How easy is it to bypass the average smartphone’s facial recognition security? In the case of Android, a lot easier than owners may think.
from Naked Security http://bit.ly/2SIGzvE
via IFTTT
Stop shaking your head about “WhatsApp Gold” flimflam and start spreading these REAL nuggets of hoax-clobbering advice!
from Naked Security http://bit.ly/2H1pOKO
via IFTTT
Australians got scary texts, emails and phone calls from a trusted emergency warning service late last week after a hacker broke into its systems and used it to send fake messages.
from Naked Security http://bit.ly/2AA1fPo
via IFTTT
In case there are some blank entries in your laundry list of New Year’s resolutions, we have a few tips for a bit of cybersecurity ‘soul searching’. Here’s the first batch, looking at how you can fix your good ol’ passwords.
The post New Year’s resolutions: Get your passwords shipshape appeared first on WeLiveSecurity
from WeLiveSecurity http://bit.ly/2SD5aSQ
via IFTTT

