The system figured out how to overcome little hurdles, like being nudged by a stuffed giraffe when trying to do important robot work.
from Naked Security https://ift.tt/2qnOpSn
via IFTTT
The system figured out how to overcome little hurdles, like being nudged by a stuffed giraffe when trying to do important robot work.
from Naked Security https://ift.tt/2qnOpSn
via IFTTT
They stole 26 million credit cards from the massive black market site, and now financial institutions are ensuring the cards can’t be abused.
from Naked Security https://ift.tt/2MRVnXa
via IFTTT
Adobe patched a total of 82 vulnerabilities across a range of products on Tuesday, including 46 critical bugs.
from Naked Security https://ift.tt/2OT0r0c
via IFTTT
ESET Smart Home Research Team uncovers Echo, Kindle versions vulnerable to 2017 Wi-Fi vulnerabilities
The post What was wrong with Alexa? How Amazon Echo and Kindle got KRACKed appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/2nRHgbV
via IFTTT
ESET researchers describe recent activity of the infamous espionage group, the Dukes, including three new malware families
The post Operation Ghost: The Dukes aren’t back – they never left appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/2oNphnq
via IFTTT
Cybercrime forums have been abuzz this week over news that BriansClub — one of the underground’s largest shops for stolen credit and debit cards — has been hacked, and its inventory of 26 million cards shared with security contacts in the banking industry. Now it appears this brazen heist may have been the result of one of BriansClub’s longtime competitors trying to knock out a rival.

And advertisement for BriansClub that for years has used my name and likeness to peddle stolen cards.
Last month, KrebsOnSecurity was contacted by an anonymous source who said he had the full database of 26M cards stolen from BriansClub, a carding site that has long used this author’s name and likeness in its advertising. The stolen database included cards added to the site between mid-2015 and August 2019.
This was a major event in the underground, as experts estimate the total number of stolen cards leaked from BriansClub represent almost 30 percent of the cards on the black market today.
The purloined database revealed BriansClub sold roughly 9.1 million stolen credit cards, earning the site and its resellers a cool $126 million in sales over four years.
In response to questions from KrebsOnSecurity, the administrator of BriansClub acknowledged that the data center serving his site had been hacked earlier in the year (BriansClub claims this happened in February), but insisted that all of the cards stolen by the hacker had been removed from BriansClub store inventories.
However, as I noted in Tuesday’s story, multiple sources confirmed they were able to find plenty of card data included in the leaked database that was still being offered for sale at BriansClub.
Perhaps inevitably, the admin of BriansClub took to the cybercrime forums this week to defend his business and reputation, re-stating his claim that all cards included in the leaked dump had been cleared from store shelves.
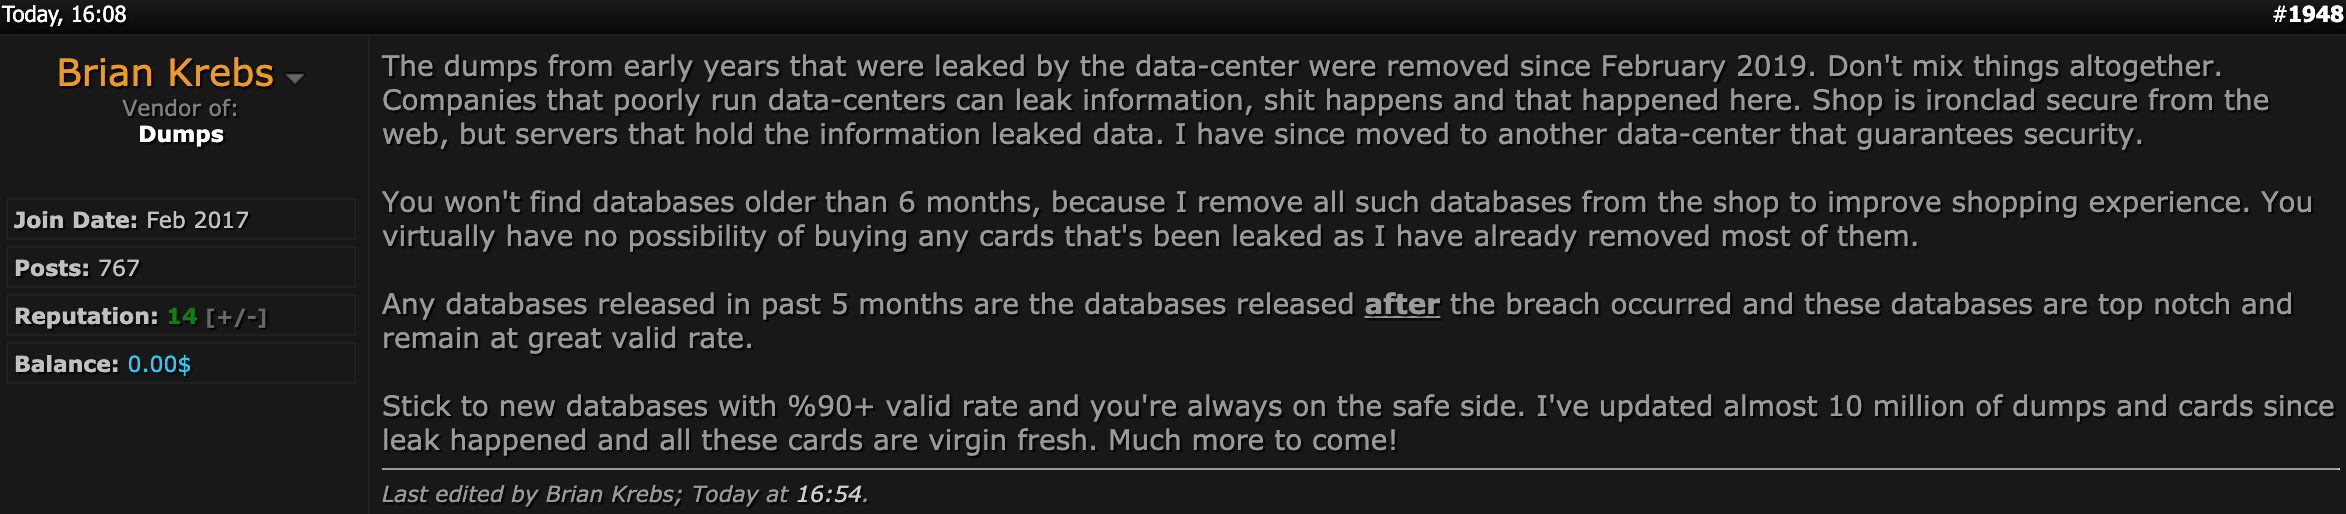
The administrator of BriansClub, who’s appropriated the name and likeness of Yours Truly for his advertising, fights to keep his business alive.
Meanwhile, some of BriansClub’s competitors gloated about the break-in. According to the administrator of Verified, one of the longest running Russian language cybercrime forums, the hack of BriansClub was perpetrated by a fairly established ne’er-do-well who uses the nickname “MrGreen” and runs a competing card shop by the same name.
The Verified site admin said MrGreen had been banned from the forum, and added that “sending anything to Krebs is the lowest of all lows” among accomplished and self-respecting cybercriminals. I’ll take that as a compliment.
This would hardly be the first time some cybercriminal has used me to take down one of his rivals. In most cases, I’m less interested in the drama and more keen on validating the data and getting it into the proper hands to do some good.
That said, if the remainder of BriansClub’s competitors want to use me to take down the rest of the carding market, I’m totally fine with that.
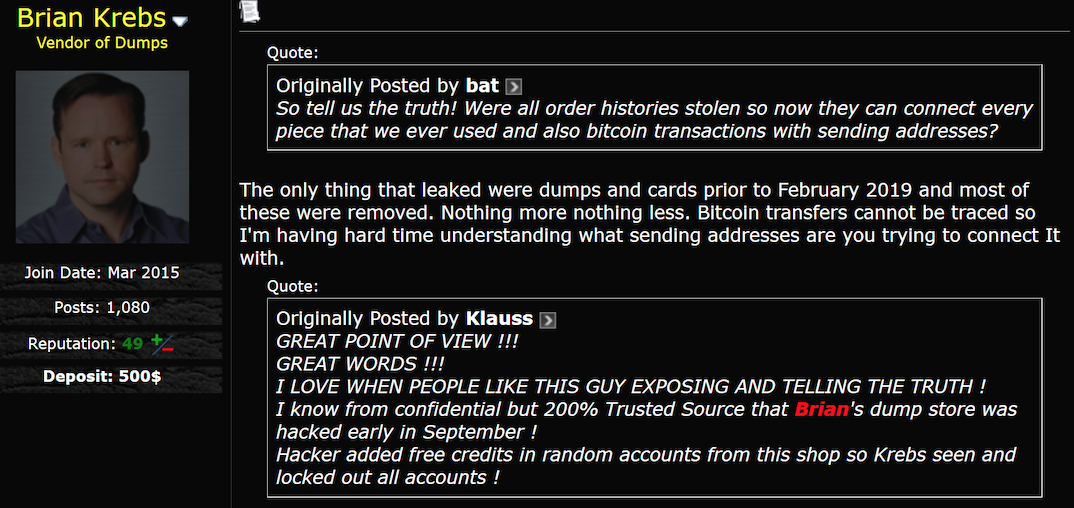
The BriansClub admin, defending the honor of his stolen cards shop after a major breach.
from Krebs on Security https://ift.tt/2Bung2x
via IFTTT
People who mistype the URL for their political candidate or party’s website could end up on an opposing party or candidate’s website, Digital Shadow’s research shows.
from Dark Reading: https://ift.tt/32nE6M5
via IFTTT
In part one of this two-part series, we start with the basics – getting everyone to understand what’s at stake – and then look at lessons from the trenches.
from Dark Reading: https://ift.tt/2Mlhfer
via IFTTT
from Dark Reading: https://ift.tt/2Ls9MeB
via IFTTT
Among the beloved entertainer’s advice: “Double bag those passwords.”Thanks, Betty.
from Dark Reading: https://ift.tt/35Hdsjx
via IFTTT

