A CASB isn’t a WAF, isn’t an NGF, and isn’t an SWG. So what is it, precisely, and why do you need one to go along with all the other letters? Read on for the answer.
from Dark Reading: https://ift.tt/2U4GPHi
via IFTTT

A CASB isn’t a WAF, isn’t an NGF, and isn’t an SWG. So what is it, precisely, and why do you need one to go along with all the other letters? Read on for the answer.
from Dark Reading: https://ift.tt/2U4GPHi
via IFTTT
COVID-19 means many people are doing their jobs from outside the confines of the office. That may not be as easy as it sounds.
from Dark Reading: https://ift.tt/2W77d64
via IFTTT
A vulnerability in Microsoft’s Server Message Block protocol prompted concerns of wormable exploits when it was disclosed this week.
from Dark Reading: https://ift.tt/39LBFGJ
via IFTTT
Cybercriminals constantly latch on to news items that captivate the public’s attention, but usually they do so by sensationalizing the topic or spreading misinformation about it. Recently, however, cybercrooks have started disseminating real-time, accurate information about global infection rates tied to the Coronavirus/COVID-19 pandemic in a bid to infect computers with malicious software.
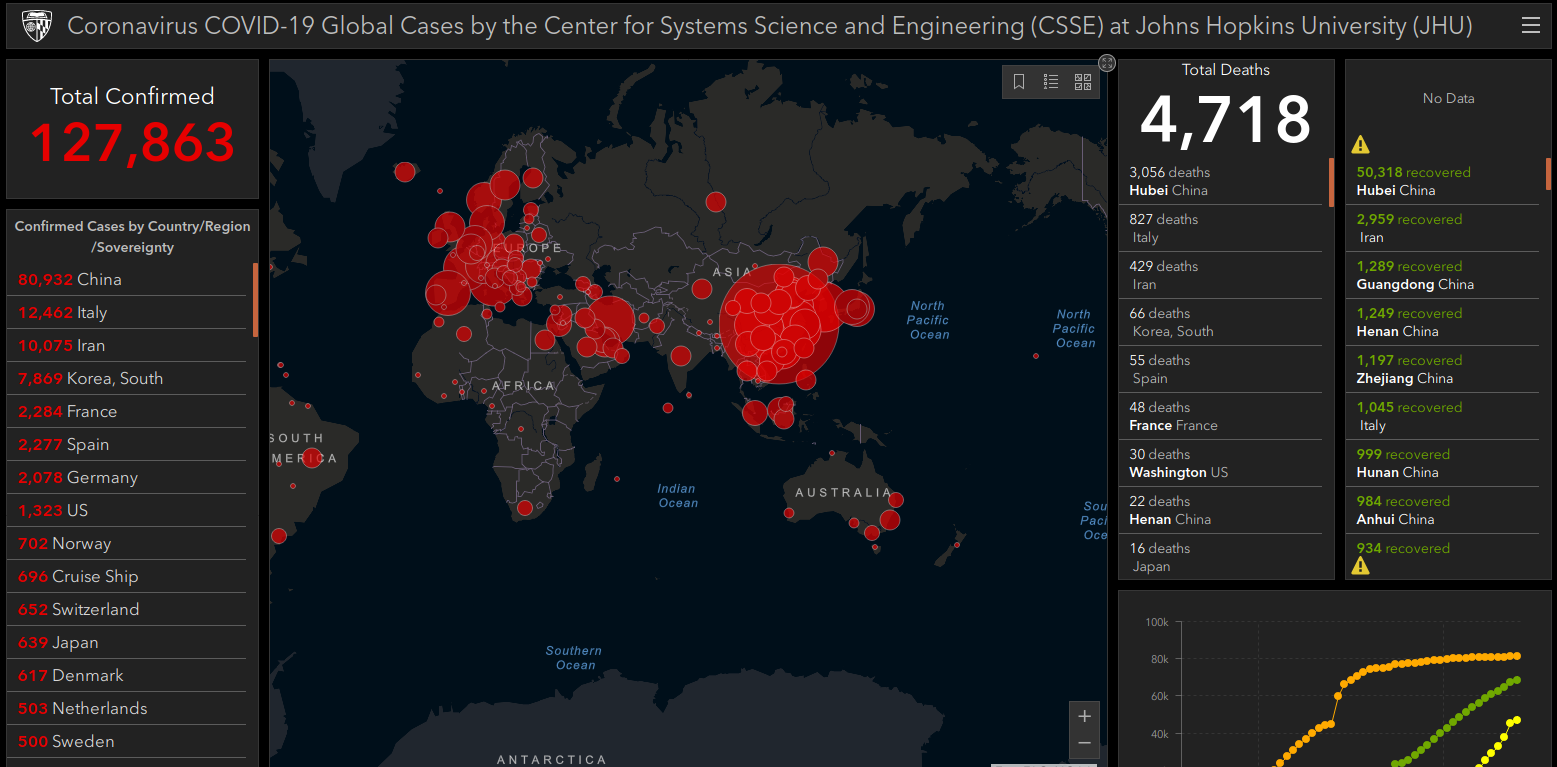
A recent snapshot of the Johns Hopkins Coronavirus data map, available at coronavirus.jhu.edu.
In one scheme, an interactive dashboard of Coronavirus infections and deaths produced by John Hopkins University is being used in malicious Web sites (and possibly spam emails) to spread password-stealing malware.
Late last month, a member of several Russian language cybercrime forums began selling a digital Coronavirus infection kit that uses the Hopkins interactive map as part of a Java-based malware deployment scheme. The kit costs $200 if the buyer already has a Java code signing certificate, and $700 if the buyer wishes to just use the seller’s certificate.
“It loads [a] fully working online map of Corona Virus infected areas and other data,” the seller explains. “Map is resizable, interactive, and has real time data from World Health Organization and other sources. Users will think that PreLoader is actually a map, so they will open it and will spread it to their friends and it goes viral!”
The sales thread claims the customer’s payload can be bundled with the Java-based map into a filename that most Webmail providers allow in sent messages. The seller claims in a demonstration video that Gmail also allows it, but the video shows Gmail still warns recipients that downloading the specific file type in question (obscured in the video) can be harmful. The seller says the user/victim has to have Java installed for the map and exploit to work, but that it will work even on fully patched versions of Java.
“Loader loads .jar files which has real working interactive Coronavirus realtime data map and a payload (can be a separate loader),” the seller said in the video. “Loader can predownload only map and payload will be loaded after the map is launched to show map faster to users. Or vice versa payload can be predownloaded and launched first.”
It’s unclear how many takers this seller has had, but earlier this week security experts began warning of new malicious Web sites being stood up that used interactive versions of the same map to distract visitors while the sites tried to foist the password-stealing AZORult malware.
As long as this pandemic remains front-page news, malware purveyors will continue to use it as lures to snare the unwary. Keep your guard up, and avoid opening attachments sent unbidden in emails — even if they appear to come from someone you know.
from Krebs on Security https://ift.tt/2Q8K53q
via IFTTT
The incident affected our office network, says ENTSO-E, as it implements measures to avoid future cyber-incursions
The post European power grid organization hit by cyberattack appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/39MDH9E
via IFTTT
Eight million customer records belonging to companies including Amazon, eBay, Shopify, PayPal, and Stripe were collected.
from Naked Security https://ift.tt/3cUUYQb
via IFTTT
A month after shipping version 73 of its Firefox browser, Mozilla has released version 74 with a range of privacy and security enhancements.
from Naked Security https://ift.tt/3cUTtl1
via IFTTT
Threat intelligence needs the problem solvers, the curious ones, the mission seekers, the analytical minds, the defenders, and the fierce — whatever their gender.
from Dark Reading: https://ift.tt/33bC5nu
via IFTTT
Intel’s March security updates reached its customers this week and the dominant theme is the bundle of flaws affecting Graphics drivers.
from Naked Security https://ift.tt/3d2MM0i
via IFTTT
Both Google and Apple have removed at least some of the apps from the company, Sensor Tower.
from Naked Security https://ift.tt/2WihFrJ
via IFTTT
 Pacosite's Blog
