macOS / iOS JavaScriptCore – Loop-Invariant Code Motion (LICM) Leaves Object Property Access Unguarded
from Exploit-DB.com RSS Feed https://ift.tt/2LO3BSg
via IFTTT

macOS / iOS JavaScriptCore – Loop-Invariant Code Motion (LICM) Leaves Object Property Access Unguarded
from Exploit-DB.com RSS Feed https://ift.tt/2LO3BSg
via IFTTT
Duo Labs’ Mikhail Davidow and Jeremy Erickson speak about their research on the Apple T2 security chip, and why they’re sharing it at Black Hat USA.
from Dark Reading: https://ift.tt/2YdZm8Z
via IFTTT
Amcrest Cameras 2.520.AC00.18.R – Unauthenticated Audio Streaming
from Exploit-DB.com RSS Feed https://ift.tt/2YwYsjo
via IFTTT
from Dark Reading: https://ift.tt/2MrACmC
via IFTTT
The PayPal Invoicing API can easily be integrated into ecommerce solution providers and others to create/send invoices
from PayPal – PayPal Stories https://ift.tt/2ZnUqek
via IFTTT
Cybercriminals are increasingly trying to trick people into paying ransoms by threatening to expose compromising activities to friends and family.
from Dark Reading: https://ift.tt/2OBJmJQ
via IFTTT
Many organizations, along with their tech teams, are questioning whether eliminating passwords as an authentication tool might augment their overall security posture.
from Dark Reading: https://ift.tt/2MpgvFH
via IFTTT
Here’s how to stop them – or at least limit the systems it can reach.
from Dark Reading: https://ift.tt/2Gyo3lK
via IFTTT
Vulnerabilities in VxWorks’ TCP stack could allow an attacker to execute random code, launch a DoS attack, or use the vulnerable system to attack other devices.
from Dark Reading: https://ift.tt/2YaDzPD
via IFTTT
Marcus Hutchins, the “accidental hero” who helped arrest the spread of the global WannaCry ransomware outbreak in 2017, will receive no jail time for his admitted role in authoring and selling malware that helped cyberthieves steal online bank account credentials from victims, a federal judge ruled Friday.
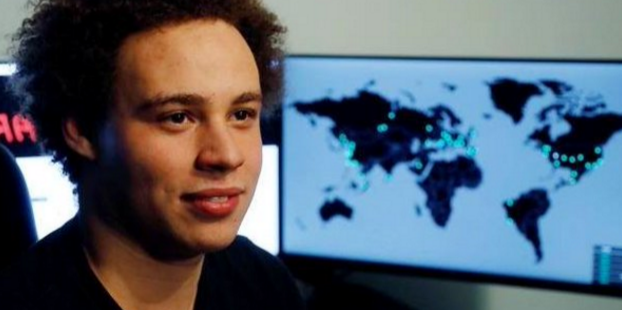
Marcus Hutchins, just after he was revealed as the security expert who stopped the WannaCry worm. Image: twitter.com/malwaretechblog
The British security enthusiast enjoyed instant fame after the U.K. media revealed he’d registered and sinkholed a domain name that researchers later understood served as a hidden “kill switch” inside WannaCry, a fast-spreading, highly destructive strain of ransomware which propagated through a Microsoft Windows exploit developed by and subsequently stolen from the U.S. National Security Agency.
In August 2017, FBI agents arrested then 23-year-old Hutchins on suspicion of authoring and spreading the “Kronos” banking trojan and a related malware tool called UPAS Kit. Hutchins was released shortly after his arrest, but ordered to remain in the United States pending trial.
Many in the security community leaped to his defense at the time, noting that the FBI’s case appeared flimsy and that Hutchins had worked tirelessly through his blog to expose cybercriminals and their malicious tools. Hundreds of people donated to his legal defense fund.
In September 2017, KrebsOnSecurity published research which strongly suggested Hutchins’ dozens of alter egos online had a fairly lengthy history of developing and selling various malware tools and services. In April 2019, Hutchins pleaded guilty to criminal charges of conspiracy and to making, selling or advertising illegal wiretapping devices.
At his sentencing hearing July 26, U.S. District Judge Joseph Peter Stadtmueller said Hutchins’ action in halting the spread of WannaCry was far more consequential than the two malware strains he admitted authoring, and sentenced him to time served plus one year of supervised release.
Marcy Wheeler, an independent journalist who live-tweeted and blogged about the sentencing hearing last week, observed that prosecutors failed to show convincing evidence of specific financial losses tied to any banking trojan victims, virtually all of whom were overseas — particularly in Hutchins’ home in the U.K.
“When it comes to matter of loss or gain,” Wheeler wrote, quoting Judge Stadtmeuller. “the most striking is comparison between you passing Kronos and WannaCry, if one looks at loss & numbers of infections, over 8B throughout world w/WannaCry, and >120M in UK.”
“This case should never have been prosecuted in the first place,” Wheeler wrote. “And when Hutchins tried to challenge the details of the case — most notably the one largely ceded today, that the government really doesn’t have evidence that 10 computers were damaged by anything Hutchins did — the government doubled down and issued a superseding indictment that, because of the false statements charge, posed a real risk of conviction.”
Hutchins’ conviction means he will no longer be allowed to stay in or visit the United States, although Judge Stadtmeuller reportedly suggested Hutchins should seek a presidential pardon, which would enable him to return and work here.
“Incredibly thankful for the understanding and leniency of the judge, the wonderful character letter you all sent, and everyone who helped me through the past two years, both financially and emotionally,” Hutchins tweeted immediately after the sentencing. “Once t[h]ings settle down I plan to focus on educational blog posts and livestreams again.”
from Krebs on Security https://ift.tt/2ZiTXKs
via IFTTT

