A team of security researchers has exploited Microsoft’s patchy macro documentation to hide malicious code inside innocent-looking macros.
from Naked Security http://bit.ly/2YbIiMz
via IFTTT
A team of security researchers has exploited Microsoft’s patchy macro documentation to hide malicious code inside innocent-looking macros.
from Naked Security http://bit.ly/2YbIiMz
via IFTTT
Government employees are working to determine the source and severity of a cyberattack that forced most city servers offline.
from Dark Reading: https://ubm.io/2V6ZFMH
via IFTTT
Companies that find a breach on their own take substantially longer to report a breach, a new analysis shows.
from Dark Reading: https://ubm.io/2PReBNL
via IFTTT
Early in the afternoon on Friday, May, 3, I asked a friend to relay a message to his security contact at CCH, the cloud-based tax division of the global information services firm Wolters Kluwer in the Netherlands. The message was that the same file directories containing new versions of CCH’s software were open and writable by any anonymous user, and that there were suspicious files in those directories indicating some user(s) abused that access.
Shortly after that report, the CCH file directory for tax software downloads was taken offline. As of this publication, several readers have reported outages affecting multiple CCH Web sites. These same readers reported being unable to access their clients’ tax data in CCH’s cloud because of the ongoing outages. A Reddit thread is full of theories.
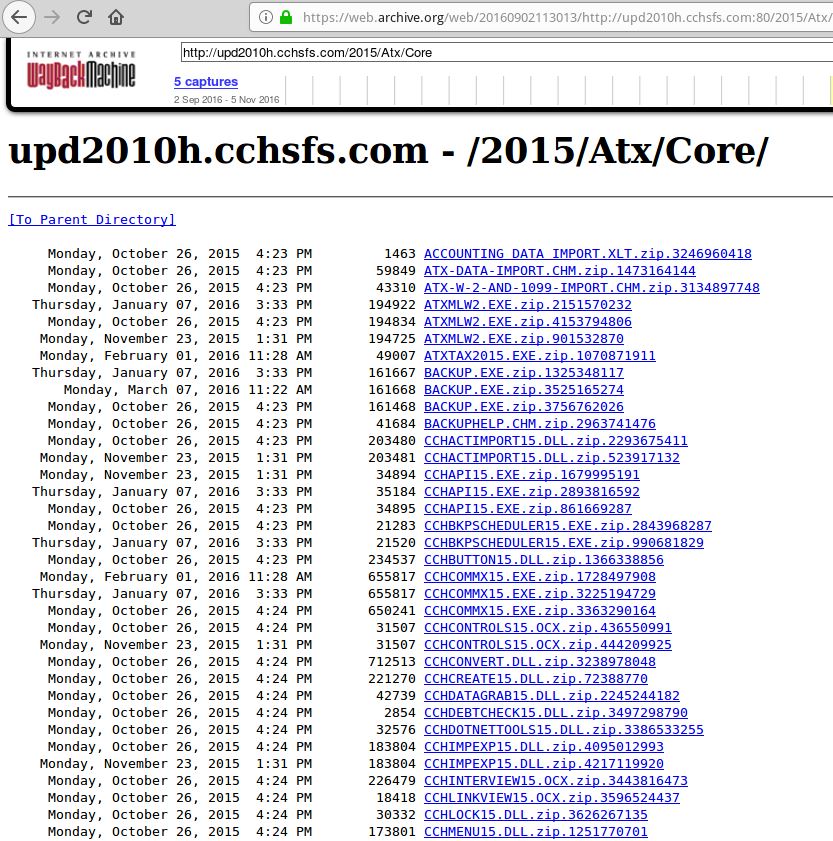
One of the many open and writable directories on CCH’s site before my report on Friday.
I do not have any information on whether my report about the world-writable file server had anything to do with the outages going on now at CCH. Nor did I see any evidence that any client data was exposed on the site.
What I did see in those CCH directories were a few odd PHP and text files, including one that seemed to be promoting two different and unrelated Russian language discussion forums.
I sent Wolters Kluwer an email asking how long the file server had been so promiscuous (allowing anyone to upload files to the server), and what the company was doing to validate the integrity of the software made available for download by CCH tax customers.
Marisa Westcott, vice president of marketing and communications at Wolters Kluwer, told KrebsOnSecurity on Friday that she would “check with the team to see if we can get some answers to your questions.”
But subsequent emails and phone calls have gone unreturned. Calls to the company’s main support number (800-739-9998) generate the voice message, “We are currently experiencing technical difficulties. Please try your call again later.”
This morning, Wolters Kluwer released an update on the extensive outage this morning on Twitter, saying:
“Since yesterday, May 6, we are experiencing network and service interruptions after certain Wolters Kluwer platforms and applications. Out of an abundance of caution, we proactively took offline a number of other applications and we immediately began our investigation and remediation efforts. The secure use of our products and services is our top priority. we have ben able to restore network and services for a number – but not all — of our systems.”
Accounting Today reports today that a PR representative from Wolters Kluwer Tax & Accounting, which makes the CCH products, confirmed the outage was the result of a malware attack:
“On Monday May 6, we started seeing technical anomalies in a number of our platforms and applications,” the statement given to Accounting Today reads. “We immediately started investigating and discovered the installation of malware. As a precaution, in parallel, we decided to take a broader range of platforms and applications offline. With this action, we aimed to quickly limit the impact this malware could have had, giving us the opportunity to investigate the issue with assistance from third-party forensics consultants and work on a solution. Unfortunately, this impacted our communication channels and limited our ability to share updates. On May 7, we were able to restore service to a number of applications and platforms.”
Accounting Today says the limited ability to share updates angered CCH users, many of whom took to social media to air their grievances against a cloud partner they perceive to be ill-prepared for maintaining ongoing service and proper security online.
“Despite CCH stating that a number of applications and platforms were up and running today, May 7, several users on a Reddit thread on the topic have stated that as of this morning in Florida, Maine, Texas, Pittsburgh and South Carolina, their CCH systems are still down,” Accounting Today wrote.
Special thanks to Alex Holden of Hold Security for help in notifying CCH.
from Krebs on Security http://bit.ly/2vJbrCr
via IFTTT
New Symantec research shows how the Buckeye group captured an exploit and backdoor used by the National Security Agency and deployed them on other victims.
from Dark Reading: https://ubm.io/2Vlsl9H
via IFTTT
New Symantec research shows how the Buckeye group captured an exploit and backdoor used by the National Security Agency and deployed them on other victims.
from Dark Reading: https://ubm.io/304HB9y
via IFTTT
Ranking based on consumers’ cybersecurity practices – or lack thereof.
from Dark Reading: https://ubm.io/2Jpmr06
via IFTTT
The number of live, accessible .onion sites amounts to less than 0.005% of surface web domains, researchers report.
from Dark Reading: https://ubm.io/2PQDZDn
via IFTTT
Criminals have begun to recognize that enterprise ransomware offers tremendous financial advantage over the more traditional tactics of wire fraud and account takeover.
from Dark Reading: https://ubm.io/2V2bT9a
via IFTTT
PayPal hosts nationwide events for U.S. merchants as part of second annual Small Business Month.
from PayPal – PayPal Stories http://bit.ly/2Vl49nT
via IFTTT

