WordPress 5.2.4 – Cross-Origin Resource Sharing
from Exploit-DB.com RSS Feed https://ift.tt/339kHz6
via IFTTT

WordPress 5.2.4 – Cross-Origin Resource Sharing
from Exploit-DB.com RSS Feed https://ift.tt/339kHz6
via IFTTT
Intelligent Security System SecurOS Enterprise 10.2 – ‘SecurosCtrlService’ Unquoted Service Path
from Exploit-DB.com RSS Feed https://ift.tt/2NvXbWj
via IFTTT
rConfig 3.9.2 – Remote Code Execution
from Exploit-DB.com RSS Feed https://ift.tt/2JBFBPy
via IFTTT
Win10 MailCarrier 2.51 – ‘POP3 User’ Remote Buffer Overflow
from Exploit-DB.com RSS Feed https://ift.tt/334GSpM
via IFTTT
PHP-FPM + Nginx – Remote Code Execution
from Exploit-DB.com RSS Feed https://ift.tt/2BV2Fob
via IFTTT
The EU has fixed a flaw in the powerful yet complex eIDAS digital identification system that let people authenticate as someone else.
from Naked Security https://ift.tt/2Ns2AgT
via IFTTT
WhatsApp has publicly attributed the attack on its users in May 2019 to the Israeli spyware makers, NSO Group.
from Naked Security https://ift.tt/2JCdQGi
via IFTTT
Is the world as we know it ready for the real impact of deepfakes?
The post DeepFakes: When seeing isn’t believing appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/36e2xxQ
via IFTTT
Most phishing kits last less than 20 days, a sign defenders are keeping up in the race against cybercrime.
from Dark Reading: https://ift.tt/2picWIs
via IFTTT
Top domain name registrars NetworkSolutions.com, Register.com and Web.com are asking customers to reset their passwords after discovering an intrusion in August 2019 in which customer account information was accessed.
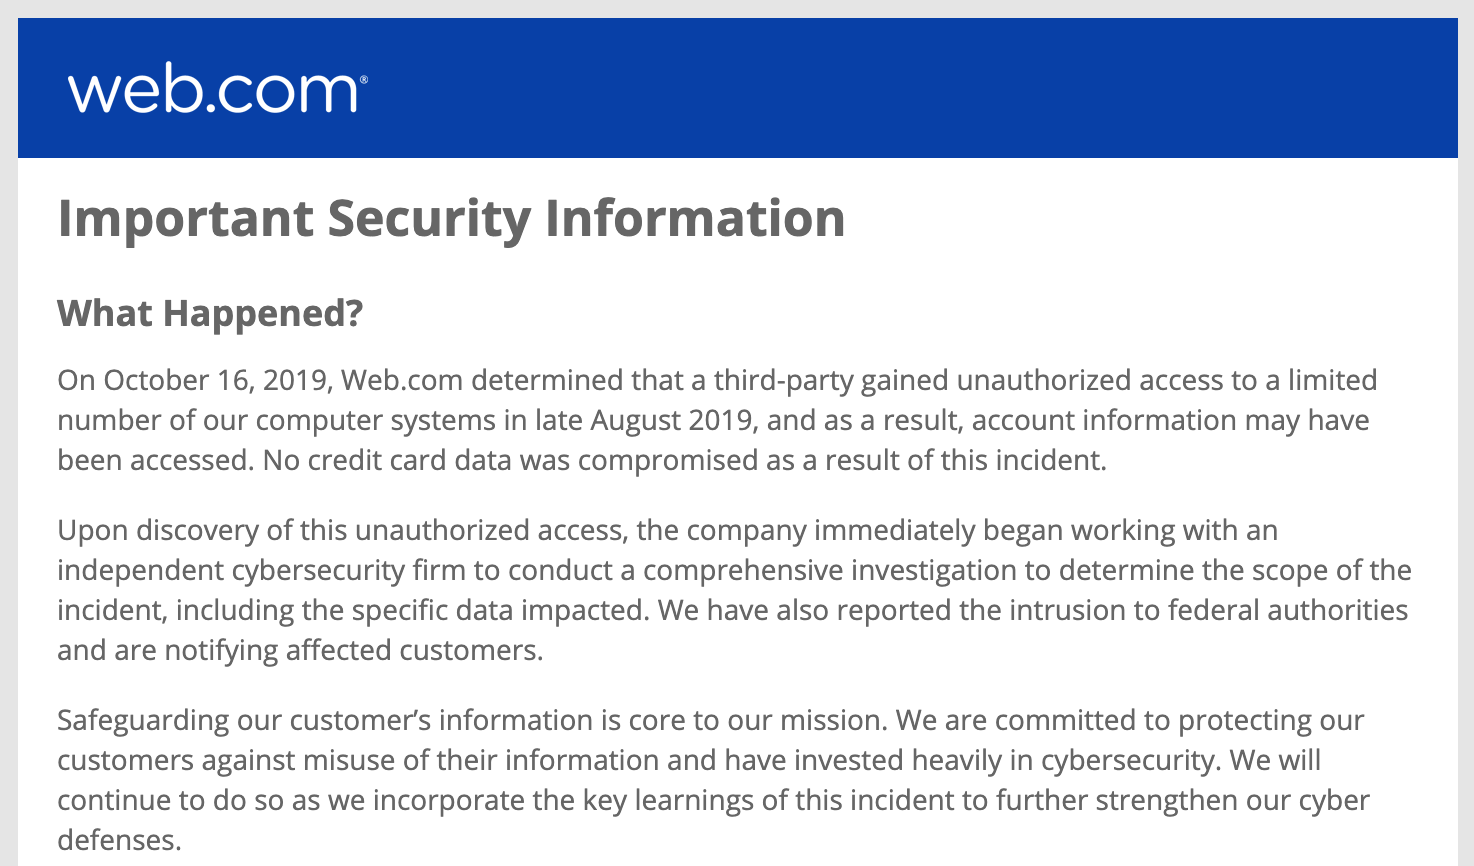
A notice to customers at notice.web.com.
“On October 16, 2019, Web.com determined that a third-party gained unauthorized access to a limited number of its computer systems in late August 2019, and as a result, account information may have been accessed,” Web.com said in a written statement. “No credit card data was compromised as a result of this incident.”
The Jacksonville, Fla.-based Web.com said the information exposed includes “contact details such as name, address, phone numbers, email address and information about the services that we offer to a given account holder.”
The “such as” wording made me ask whether the company has any reason to believe passwords — scrambled or otherwise — were accessed.
A spokesperson for Web.com later clarified that the company does not believe customer passwords were accessed.
“We encrypt account passwords and do not believe this information is vulnerable as a specific result of this incident. As an added precautionary measure, customers will be required to reset passwords the next time they log in to their accounts. As with any online service or platform, it is also good security practice to change passwords often and use a unique password for each service.”
Both Network Solutions and Register.com are owned by Web.com. Network Solutions is now the world’s fifth-largest domain name registrar, with almost seven million domains in its stable, according to domainstate.com; Register.com listed at #17 with 1.7 million domains.
Web.com’s homepage currently makes no mention of the breach notification.
NetworkSolutions.com does not appear to currently link to any information about the incident on its homepage, nor does Web.com. To get to the advisory, one needs to visit notice.web.com.
Web.com said it has reported the incident to law enforcement and hired an outside security firm to investigate further, and is in the process of notifying affected customers through email and via its website.
The company says it plans to circle back with customers when it learns the results of its investigation, but I wonder whether we’ll ever hear more about this breach.
Web.com wasn’t clear how long the intrusion lasted, but if the breach wasn’t detected until mid-October that means the intruders potentially had about six weeks inside unnoticed. That’s a long time for an adversary to wander about one’s network, and plenty of time to steal a great deal more information than just names, addresses and phone numbers.
H/T to domaininvesting.com‘s Elliot Silver for the heads up on this notification.
from Krebs on Security https://ift.tt/2MY3pz3
via IFTTT

