Most of the malware used in attacks last quarter were designed to evade signature-based detection tools, WatchGuard says.
from Dark Reading: https://ift.tt/340myb1
via IFTTT
Most of the malware used in attacks last quarter were designed to evade signature-based detection tools, WatchGuard says.
from Dark Reading: https://ift.tt/340myb1
via IFTTT
Turns out, creating wireless ecosystems for a vast number of different architectures, configurations, and use cases is hard.
from Dark Reading: https://ift.tt/3hWDPXn
via IFTTT
A now-patched remote code execution vulnerability could be exploited with a specially sized image file, researchers report.
from Dark Reading: https://ift.tt/3i2983g
via IFTTT
CrowdStrike plans to use Preempt Security’s conditional access technology to strengthen its Falcon platform.
from Dark Reading: https://ift.tt/365Waiy
via IFTTT
More explicit threat models can make security better and open the door to real and needed innovation.
from Dark Reading: https://ift.tt/3i0P69p
via IFTTT
Microsoft warned on Wednesday that malicious hackers are exploiting a particularly dangerous flaw in Windows Server systems that could be used to give attackers the keys to the kingdom inside a vulnerable corporate network. Microsoft’s warning comes just days after the U.S. Department of Homeland Security issued an emergency directive instructing all federal agencies to patch the vulnerability by Sept. 21 at the latest.
DHS’s Cybersecurity and Infrastructure Agency (CISA) said in the directive that it expected imminent exploitation of the flaw — CVE-2020-1472 and dubbed “ZeroLogon” — because exploit code which can be used to take advantage of it was circulating online.
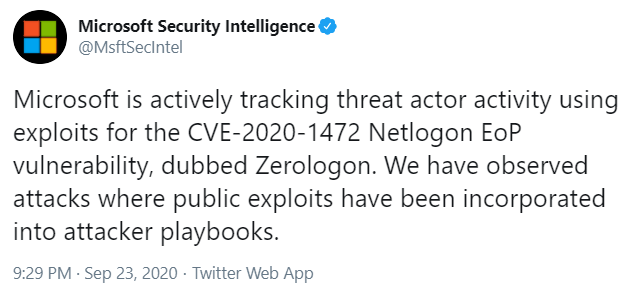
Last night, Microsoft’s Security Intelligence unit tweeted that the company is “tracking threat actor activity using exploits for the CVE-2020-1472 Netlogon vulnerability.”
“We have observed attacks where public exploits have been incorporated into attacker playbooks,” Microsoft said. “We strongly recommend customers to immediately apply security updates.”
Microsoft released a patch for the vulnerability in August, but it is not uncommon for businesses to delay deploying updates for days or weeks while testing to ensure the fixes do not interfere with or disrupt specific applications and software.
CVE-2020-1472 earned Microsoft’s most-dire “critical” severity rating, meaning attackers can exploit it with little or no help from users. The flaw is present in most supported versions of Windows Server, from Server 2008 through Server 2019.
The vulnerability could let an unauthenticated attacker gain administrative access to a Windows domain controller and run an application of their choosing. A domain controller is a server that responds to security authentication requests in a Windows environment, and a compromised domain controller can give attackers the keys to the kingdom inside a corporate network.
Scott Caveza, research engineering manager at security firm Tenable, said several samples of malicious .NET executables with the filename ‘SharpZeroLogon.exe’ have been uploaded to VirusTotal, a service owned by Google that scans suspicious files against dozens of antivirus products.
“Given the flaw is easily exploitable and would allow an attacker to completely take over a Windows domain, it should come as no surprise that we’re seeing attacks in the wild,” Caveza said. “Administrators should prioritize patching this flaw as soon as possible. Based on the rapid speed of exploitation already, we anticipate this flaw will be a popular choice amongst attackers and integrated into malicious campaigns.”
from Krebs on Security https://ift.tt/306jyZl
via IFTTT
CrowdStrike plans to use Preemptive Security’s conditional access technology to strengthen its Falcon platform.
from Dark Reading: https://ift.tt/363dJ2I
via IFTTT
The Security Intelligence team at Microsoft is tracking newly waged exploits in the wild.
from Dark Reading: https://ift.tt/362rRJt
via IFTTT
Visitor Management System in PHP 1.0 – Persistent Cross-Site Scripting
from Exploit-DB.com RSS Feed https://ift.tt/2G3wRTh
via IFTTT
Simple Online Food Ordering System 1.0 – ‘id’ SQL Injection (Unauthenticated)
from Exploit-DB.com RSS Feed https://ift.tt/3kQ4N57
via IFTTT
 Pacosite's Blog
