Vulnerabilities in VxWorks’ TCP stack could allow an attacker to execute random code, launch a DoS attack, or use the vulnerable system to attack other devices.
from Dark Reading: https://ift.tt/2YaDzPD
via IFTTT

Vulnerabilities in VxWorks’ TCP stack could allow an attacker to execute random code, launch a DoS attack, or use the vulnerable system to attack other devices.
from Dark Reading: https://ift.tt/2YaDzPD
via IFTTT
Marcus Hutchins, the “accidental hero” who helped arrest the spread of the global WannaCry ransomware outbreak in 2017, will receive no jail time for his admitted role in authoring and selling malware that helped cyberthieves steal online bank account credentials from victims, a federal judge ruled Friday.
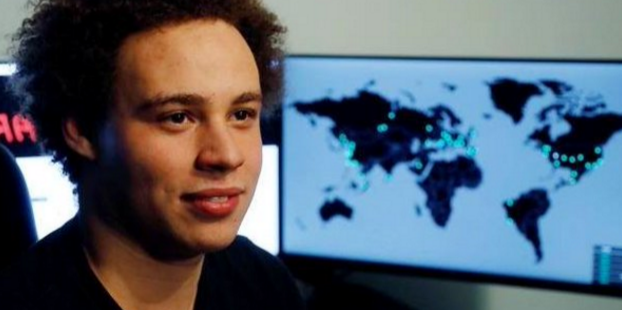
Marcus Hutchins, just after he was revealed as the security expert who stopped the WannaCry worm. Image: twitter.com/malwaretechblog
The British security enthusiast enjoyed instant fame after the U.K. media revealed he’d registered and sinkholed a domain name that researchers later understood served as a hidden “kill switch” inside WannaCry, a fast-spreading, highly destructive strain of ransomware which propagated through a Microsoft Windows exploit developed by and subsequently stolen from the U.S. National Security Agency.
In August 2017, FBI agents arrested then 23-year-old Hutchins on suspicion of authoring and spreading the “Kronos” banking trojan and a related malware tool called UPAS Kit. Hutchins was released shortly after his arrest, but ordered to remain in the United States pending trial.
Many in the security community leaped to his defense at the time, noting that the FBI’s case appeared flimsy and that Hutchins had worked tirelessly through his blog to expose cybercriminals and their malicious tools. Hundreds of people donated to his legal defense fund.
In September 2017, KrebsOnSecurity published research which strongly suggested Hutchins’ dozens of alter egos online had a fairly lengthy history of developing and selling various malware tools and services. In April 2019, Hutchins pleaded guilty to criminal charges of conspiracy and to making, selling or advertising illegal wiretapping devices.
At his sentencing hearing July 26, U.S. District Judge Joseph Peter Stadtmueller said Hutchins’ action in halting the spread of WannaCry was far more consequential than the two malware strains he admitted authoring, and sentenced him to time served plus one year of supervised release.
Marcy Wheeler, an independent journalist who live-tweeted and blogged about the sentencing hearing last week, observed that prosecutors failed to show convincing evidence of specific financial losses tied to any banking trojan victims, virtually all of whom were overseas — particularly in Hutchins’ home in the U.K.
“When it comes to matter of loss or gain,” Wheeler wrote, quoting Judge Stadtmeuller. “the most striking is comparison between you passing Kronos and WannaCry, if one looks at loss & numbers of infections, over 8B throughout world w/WannaCry, and >120M in UK.”
“This case should never have been prosecuted in the first place,” Wheeler wrote. “And when Hutchins tried to challenge the details of the case — most notably the one largely ceded today, that the government really doesn’t have evidence that 10 computers were damaged by anything Hutchins did — the government doubled down and issued a superseding indictment that, because of the false statements charge, posed a real risk of conviction.”
Hutchins’ conviction means he will no longer be allowed to stay in or visit the United States, although Judge Stadtmeuller reportedly suggested Hutchins should seek a presidential pardon, which would enable him to return and work here.
“Incredibly thankful for the understanding and leniency of the judge, the wonderful character letter you all sent, and everyone who helped me through the past two years, both financially and emotionally,” Hutchins tweeted immediately after the sentencing. “Once t[h]ings settle down I plan to focus on educational blog posts and livestreams again.”
from Krebs on Security https://ift.tt/2ZiTXKs
via IFTTT
Failures in computer and control systems are being blamed.
from Dark Reading: https://ift.tt/2GAUvEa
via IFTTT
The data breach compromised data belonging to customers in parts of Southeast Asia, Australia, and New Zealand.
from Dark Reading: https://ift.tt/2SPBK4B
via IFTTT
ESET researchers discover a new Android ransomware family that attempts to spread to victims’ contacts and deploys some unusual tricks
The post Android ransomware is back appeared first on WeLiveSecurity
from WeLiveSecurity https://ift.tt/2K2DKnv
via IFTTT
It’s Shark Week again! Are you ready to outmaneuver sharks of the cyber variety? These tips can help.
from Dark Reading: https://ift.tt/2ylrAzj
via IFTTT
WP Database Backup < 5.2 – Remote Code Execution (Metasploit)
from Exploit-DB.com RSS Feed https://ift.tt/2YuqDU4
via IFTTT
Schneider Electric Pelco Endura NET55XX Encoder – Authentication Bypass (Metasploit)
from Exploit-DB.com RSS Feed https://ift.tt/2LNPUmi
via IFTTT
The Senate Intelligence Committee doesn’t know what Moscow’s intentions are, but Robert Mueller says they’re still at it.
from Naked Security https://ift.tt/2YxToLK
via IFTTT
Cybercriminals are targeting numerous Network Attached Storage vendors with a new wave of ransomware.
from Naked Security https://ift.tt/2K6Vf4Q
via IFTTT

