As the CIO for both Formula 1 and NASCAR racing teams, Gary Foote is tackling the same security issues as other manufacturing CIOs — with a huge dash of motorized mayhem thrown in.
from Dark Reading: https://ift.tt/2P87Uu5
via IFTTT
As the CIO for both Formula 1 and NASCAR racing teams, Gary Foote is tackling the same security issues as other manufacturing CIOs — with a huge dash of motorized mayhem thrown in.
from Dark Reading: https://ift.tt/2P87Uu5
via IFTTT
Criminals appear to have developed it knowing some users have not patched or updated to newer versions, Trend Micro says.
from Dark Reading: https://ift.tt/33Vjb47
via IFTTT
Lorem Ipsum is simply dummy text of the printing and typesetting industry. Lorem Ipsum has been the industry’s standard dummy text ever since the 1500s, when an unknown printer took a galley of type and scrambled it to make a type specimen book
from Dark Reading: https://ift.tt/2ljwp9i
via IFTTT
from Dark Reading: https://ift.tt/2MrACmC
via IFTTT
On Tuesday of this week, one of the more popular underground stores peddling credit and debit card data stolen from hacked merchants announced a blockbuster new sale: More than 5.3 million new accounts belonging to cardholders from 35 U.S. states. Multiple sources now tell KrebsOnSecurity that the card data came from compromised gas pumps, coffee shops and restaurants operated by Hy-Vee, an Iowa-based company that operates a chain of more than 245 supermarkets throughout the Midwestern United States.
Hy-Vee, based in Des Moines, announced on Aug. 14 it was investigating a data breach involving payment processing systems that handle transactions at some Hy-Vee fuel pumps, drive-thru coffee shops and restaurants.
The restaurants affected include Hy-Vee Market Grilles, Market Grille Expresses and Wahlburgers locations that the company owns and operates. Hy-Vee said it was too early to tell when the breach initially began or for how long intruders were inside their payment systems.
But typically, such breaches occur when cybercriminals manage to remotely install malicious software on a retailer’s card-processing systems. This type of point-of-sale malware is capable of copying data stored on a credit or debit card’s magnetic stripe when those cards are swiped at compromised payment terminals. This data can then be used to create counterfeit copies of the cards.
Hy-Vee said it believes the breach does not affect payment card terminals used at its grocery store checkout lanes, pharmacies or convenience stores, as these systems rely on a security technology designed to defeat card-skimming malware.
“These locations have different point-of-sale systems than those located at our grocery stores, drugstores and inside our convenience stores, which utilize point-to-point encryption technology for processing payment card transactions,” Hy-Vee said. “This encryption technology protects card data by making it unreadable. Based on our preliminary investigation, we believe payment card transactions that were swiped or inserted on these systems, which are utilized at our front-end checkout lanes, pharmacies, customer service counters, wine & spirits locations, floral departments, clinics and all other food service areas, as well as transactions processed through Aisles Online, are not involved.”
According to two sources who asked not to be identified for this story — including one at a major U.S. financial institution — the card data stolen from Hy-Vee is now being sold under the code name “Solar Energy,” at the infamous Joker’s Stash carding bazaar.
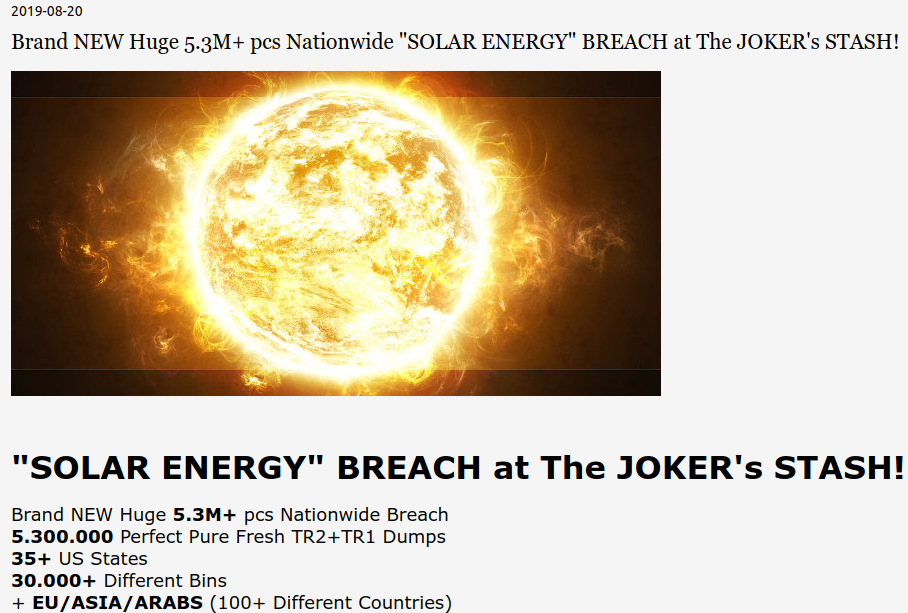
An ad at the Joker’s Stash carding site for “Solar Energy,” a batch of more than 5 million credit and debit cards sources say was stolen from customers of supermarket chain Hy-Vee.
Hy-Vee said the company’s investigation is continuing.
“We are aware of reports from payment processors and the card networks of payment data being offered for sale and are working with the payment card networks so that they can identify the cards and work with issuing banks to initiate heightened monitoring on accounts,” Hy-Vee spokesperson Tina Pothoff said.
The card account records sold by Joker’s Stash, known as “dumps,” apparently stolen from Hy-Vee are being sold for prices ranging from $17 to $35 apiece. Buyers typically receive a text file that includes all of their dumps. Those individual dumps records — when encoded onto a new magnetic stripe on virtually anything the size of a credit card — can be used to purchase stolen merchandise in big box stores.
As noted in previous stories here, the organized cyberthieves involved in stealing card data from main street merchants have gradually moved down the food chain from big box retailers like Target and Home Deport to smaller but far more plentiful and probably less secure merchants (either by choice or because the larger stores became a harder target).
It’s really not worth spending time worrying about where your card number may have been breached, since it’s almost always impossible to say for sure and because it’s common for the same card to be breached at multiple establishments during the same time period.
Just remember that while consumers are not liable for fraudulent charges, it may still fall to you the consumer to spot and report any suspicious charges. So keep a close eye on your statements, and consider signing up for text message notifications of new charges if your card issuer offers this service. Most of these services also can be set to alert you if you’re about to miss an upcoming payment, so they can also be handy for avoiding late fees and other costly charges.
from Krebs on Security https://ift.tt/2TV0IjC
via IFTTT
Some aviation experts and security researchers are trying to foster closer alliances for securing airplane networks.
from Dark Reading: https://ift.tt/2MxqhGE
via IFTTT
Bad actors move faster than threat intelligence feeds and the infosec pros who monitor them, notes Joakim Kennedy, Threat Intel Manager for Anomali Research. Organizations need to establish a dedicated team to manage threat intel, and an adequate budget. Kennedy also encourages intelligence sharing as part of a stepped-up protection strategy.
from Dark Reading: https://ift.tt/2MxppSo
via IFTTT
Microsoft remains the favorite brand to spoof in phishing campaigns, but more attackers are impersonating Facebook.
from Dark Reading: https://ift.tt/30B8l1r
via IFTTT
Employees at Portland Public Schools were breathing easier this week after thwarting a business email compromise (BEC) scam that could have cost them almost $3m.
from Naked Security https://ift.tt/33P4saY
via IFTTT
Microsoft has given audio clips to contractors for years, but it says it recently stopped. … For the most part.
from Naked Security https://ift.tt/2MxD2Rv
via IFTTT

